Layover is a Linux machine with Medium level complexity.
We start the machine with some credentials of an account:
contractor : Contractor2026!
Initial nmap scan reveals port 22 and port 3389 open.
Port 3389 is the default network port used by Microsoft's Remote Desktop Protocol (RDP) for both TCP and UDP connections.
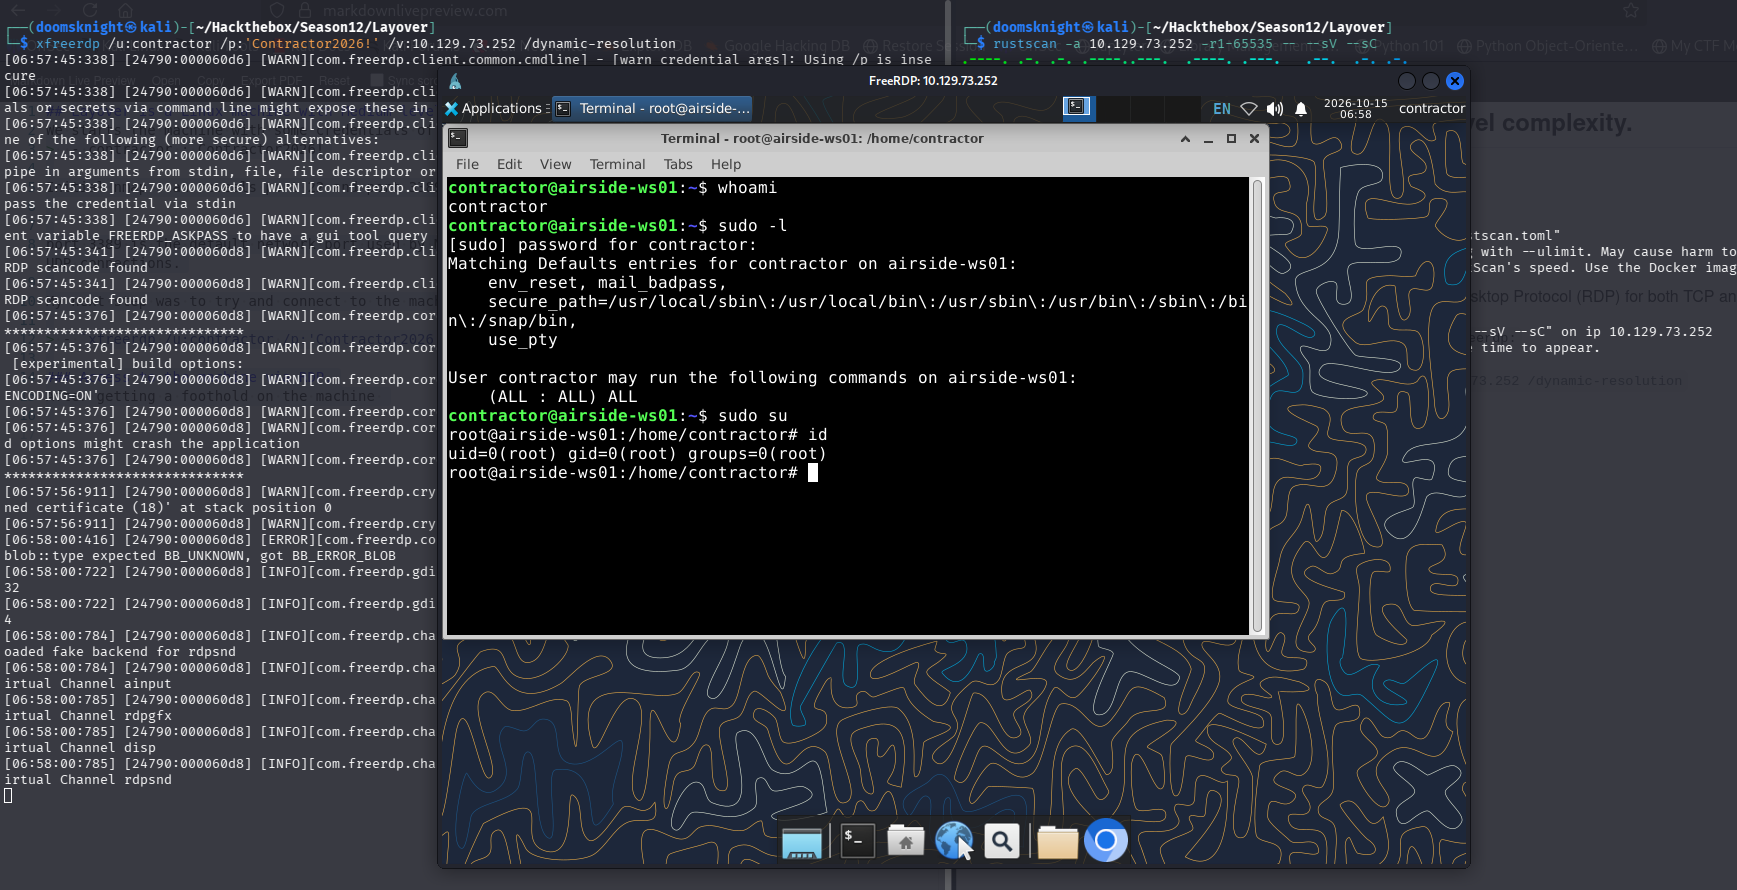
My next step was to try and connect to the machine via RDP using xfreerdp:
xfreerdp /u:contractor /p:'Contractor2026!' /v:10.129.73.252 /dynamic-resolution
Access to the machine via RDP
After getting a foothold on the machine, we found that we can get full access by just running sudo su and using Contractor2026! as the password.
This was so simple for a medium level machine. Furthermore, we don't have a user flag or root flag yet, so this must be just an initial foothold and we need to do further enumeration from this particular step.